> For the complete documentation index, see [llms.txt](https://docs.p0.dev/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.p0.dev/integrations/resource-integrations/aws.md).
# AWS
Install P0 IAM management on AWS in about 10 minutes. Configure just-in-time access, identity governance, and privilege management for your AWS environment.
The AWS integration lets P0 grant just-in-time, least-privileged access to your AWS accounts. It has two components:
* **IAM management** provisions and revokes access for your users. Installing it takes about 10 minutes.
* **Resource inventory** extends IAM management with fine-grained, resource-level access.
### Setting up AWS IAM management
To install the IAM management component and choose how P0 provisions your users, see [Setting up AWS IAM management](/integrations/resource-integrations/aws/installation-methods.md). You choose one of these login types during setup:
* [IAM](/integrations/resource-integrations/aws/installation-methods/iam.md) — provision users defined in the account's IAM service.
* [Identity Center](/integrations/resource-integrations/aws/installation-methods/identity-center.md) — provision users through AWS Identity Center.
* [Federated](/integrations/resource-integrations/aws/installation-methods/federated.md) — provision users through an Okta SAML federation.
To provision access through a single shared Identity Center permission set instead, use the [Identity Center (merged)](/integrations/resource-integrations/aws/identity-center-merged.md) integration (beta).
### Setting up AWS resource inventory
Installing P0 resource inventory on AWS takes about 10 minutes.
The resource inventory component extends the IAM management integration and allows requesting [fine-grained resource-level](/integrations/resource-integrations/aws/requesting-access.md#fine-grained-resource-level-access) access in AWS.
{% hint style="info" %}
An installed AWS IAM management integration is required
{% endhint %}
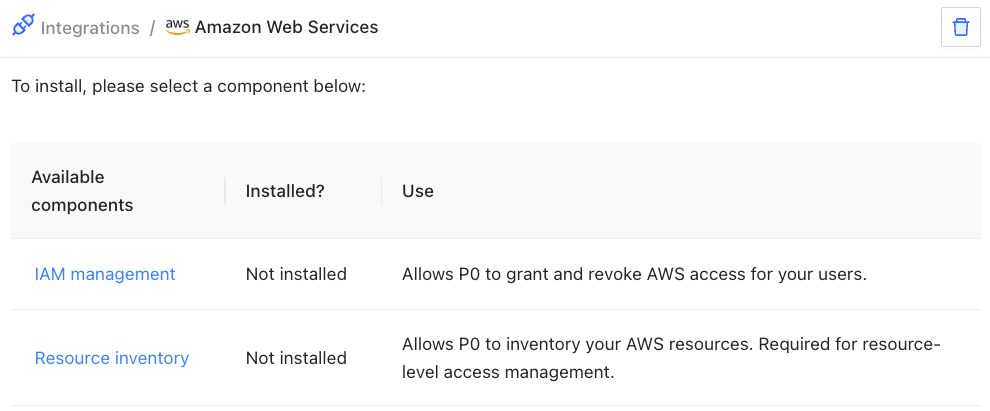
1. Navigate to "Integrations" on [p0.app](https://p0.app), then select "Amazon Web Services". Choose the "Resource inventory" component:
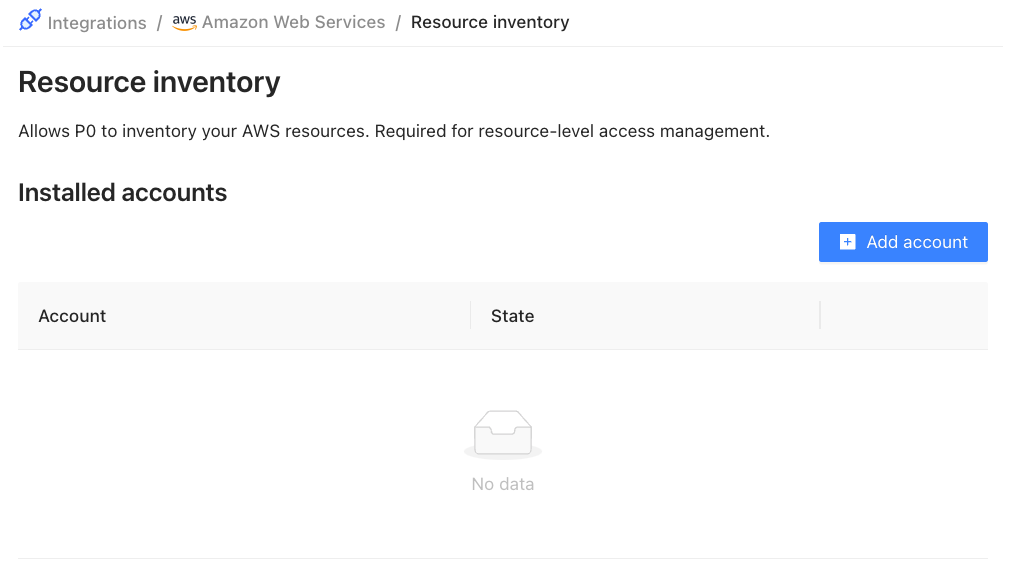
2. Click "Add account"
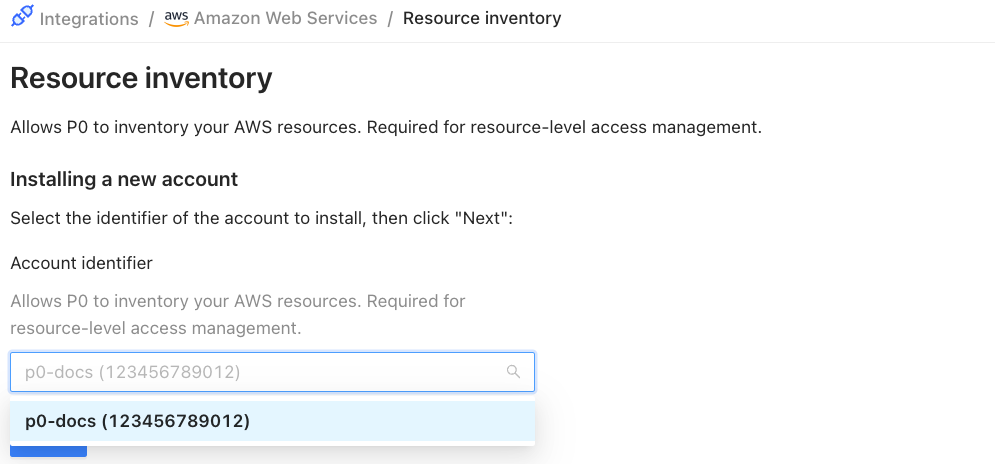
3. Choose one of the AWS accounts already installed for IAM management:
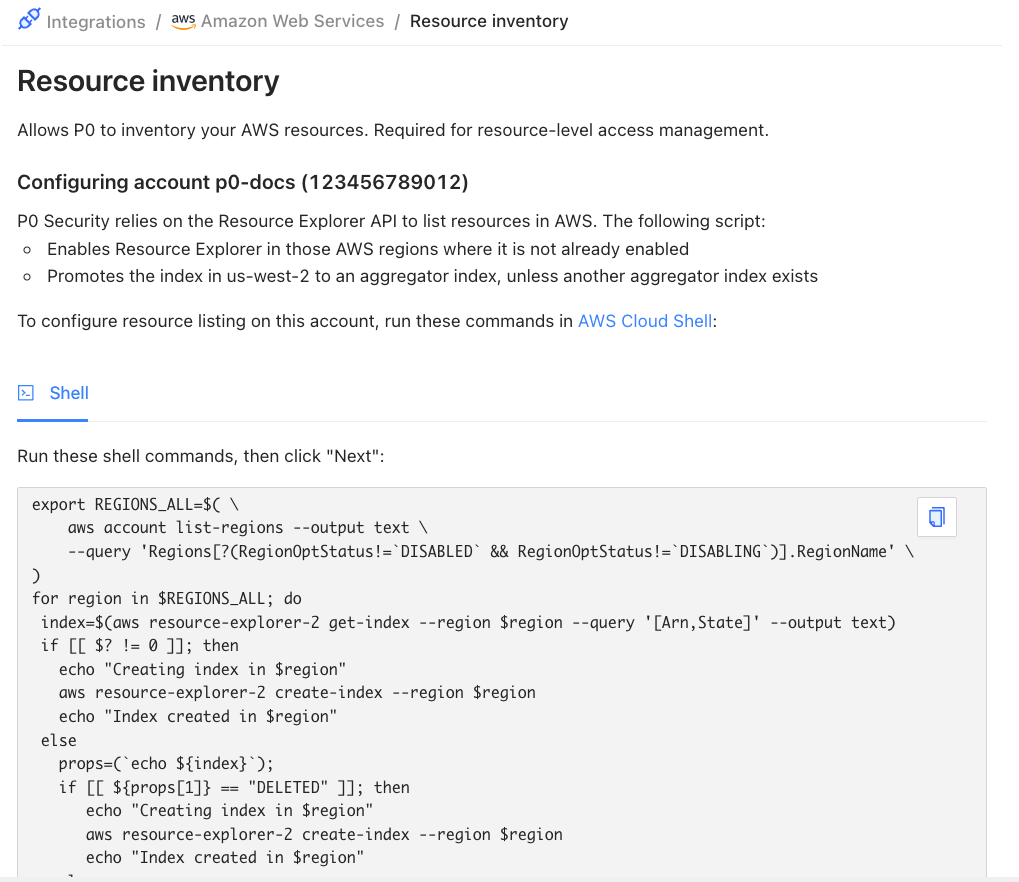
4. Run the AWS CLI commands to configure Resource Explorer
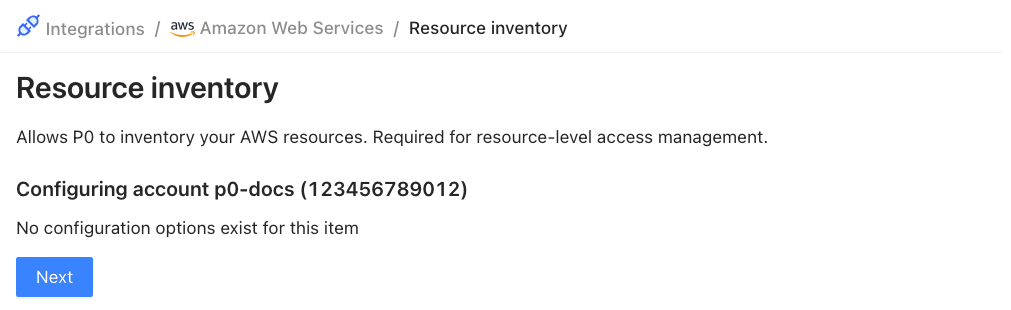
5. Click "Next" to validate your setup. You will land on the resource inventory configuration page. Clicking "Next" again takes you back to the Resource inventory overview page.
And that's it. You're all set to start granting just-in-time, least-privileged access to AWS with P0.